
The issues came to light as part of Cisco’s effort to ensure proactive security and product quality. To that end, teams for Cisco Emergency Responder, Cisco Prime Collaboration Deployment, Cisco Unified Communications Manager (Unified CM), Cisco Unified Communications Manager IM & Presence Service (Unified CM IM&P), Cisco Unified Communications Manager Session Management Edition (Unified CM SME), and Cisco Unity Connection conducted a comprehensive internal security review.
This review resulted in software hardening releases that address multiple internally discovered vulnerabilities. These vulnerabilities ended up found during internal testing and they do not appear to be undergoing active exploitation.
Cisco released software updates that address these vulnerabilities, according to an advisory. There are no workarounds that address these vulnerabilities.
These vulnerabilities affect the following Cisco products, regardless of device configuration:

- Emergency Responder
- Prime Collaboration Deployment
- Unified CM
- Unified CM IM&P
- Unified CM SME
- Unity Connection
Vulnerabilities
In one issue, there is an improper neutralization of special elements in output used by a downstream component.
CVE-2026-76473 is the case number for the vulnerability which has a CVSS base score of 9.8.
Additionally, there is an improper authentication that covers bypasses, session fixation, spoofing, and capture replay.
CVE-2026-76474 is the case number for the vulnerability which has a CVSS base score of 9.8.
Also, there is an improper neutralization of input during web page generation.
CVE-2026-76475 is the case number for the vulnerability which has a CVSS base score of 9.3.
Meanwhile, there is an improper input validation.
CVE-2026-76476 is the case number for the vulnerability which has a CVSS base score of 8.8.
Moreover, there is an improper neutralization of special elements used in an SQL command.
CVE-2026-76477 is the case number for the vulnerability which has a CVSS base score of 8.8.
Furthermore, there is an improper access control, which covers authorization, authentication, privileges, and bypasses.
CVE-2026-76478 is the case number for the vulnerability which has a CVSS base score of 8.8.
Indeed, there is an improper limitation of a pathname to a restricted directory.
CVE-2026-76479 is the case number for the vulnerability which has a CVSS base score of 7.8.
Additionally, there is an improper handling of exceptional conditions, which covers uncaught exceptions and reachable assertions.
CVE-2026-76481 is the case number for the vulnerability which has a CVSS base score of 7.5.
There are no workarounds that address these vulnerabilities.
Fixed Versions
In the table below, the left column lists Cisco software releases. The right column indicates the first release that includes the fix for these vulnerabilities.
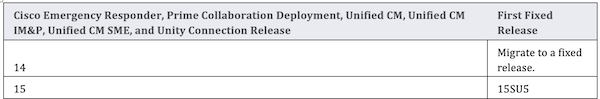
Cisco PSIRT is not aware of any public announcements or malicious use of the vulnerabilities.
Click here for additional information on other Cisco security updates.