
Critical infrastructure includes things like the power grid, gas and oil pipelines, military installations and hospitals. An example of a recent attack on critical infrastructure is the ransomware attack on the Colonial Pipeline last year. The attack on computerized equipment left the pipeline down for six days while the company forked over an estimated $4.4 million in Bitcoin to pay the attackers (though much of it was subsequently recovered).
To that end, that is why the National Centers of Academic Excellence in Cybersecurity, located within the National Security Agency, awarded $637,223 to Brajendra Panda, a professor of computer science and computer engineering at the University of Arkansas.
In his proposal, Panda said the interdependence and interconnection of critical infrastructure systems make them more vulnerable to cyberattacks and can cause initial damage to spread quickly to other systems.

“Thus, a small vulnerability in one of these systems can result in crippling a large number of them,” Panda said. “These systems are of heterogeneous type by nature, meaning they contain both heterogeneous software and data.”
Due to the complexity of critical infrastructure systems, recovering them can cause significant delays, which is concerning given the time-sensitive nature of the functions these systems provide, such as electricity.
Panda’s goal is to develop fast, accurate and efficient recovery mechanisms that, when coupled with the expeditious damage assessment techniques he has already developed, will offer an “integrated suite solution.”
This will allow affected critical infrastructure systems to continue running while providing as many critical functionalities as possible.
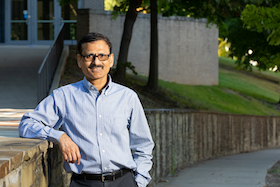
Brajendra Panda won a grant to improve recovery methods for critical infrastructure following a cyberattack.
Source: University of Arkansas
The two-year grant, with an option for a third year, builds on a previous $287,000 grant from the same funding agency that focused on expediting assessment of damage following a cyber-attack.