
Since 2018, Gootloader malware infected at least 25,000 computers around the world. Gootloader malware has been used in ransomware attacks of at least 44 U.S. based victims which has resulted in $28.8 million in losses.
Gootloader is malware that infects victim computers through a variety of means, often by tricking unsuspecting individuals into downloading it, according to warrants unsealed this week.
“With court authorization, the Department of Justice and FBI, along with our international partners, conducted an online operation that liberated over 100 servers from malicious software, denying ransomware criminals a platform,” said Assistant Attorney General A. Tysen Duva of the Justice Department’s Criminal Division.

Global Partnerships
“Cybercrime knows no borders and this case is an excellent example of international partnerships working to protect people around the world,” said U.S. Attorney Peter McNeilly for the District of Colorado.
“The Gootloader malware targeted victims on a global scale, including attacks on the U.S. Department of War and the Defense Industrial Base,” said Special Agent in Charge Kenneth DeChellis of the Department of Defense Office of Inspector General Defense Criminal Investigative Service (DCIS), Cyber Field Office.
“Using a network of compromised websites, Gootloader malware infected thousands of computers worldwide, providing cybercriminals with access to deploy ransomware and cause millions of dollars in losses,” said Operations Director Brett Leatherman of the FBI Cyber Branch. “Working alongside our partners, we disrupted the Gootloader botnet through coordinated technical operations, victim notifications, and remediation. Strong international and private-sector partnerships made this disruption possible, allowing us to protect victims from further harm and prevent future exploitation.”
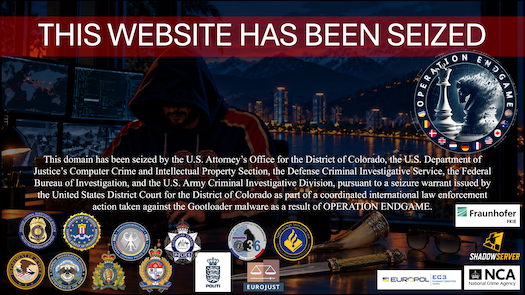
Banner that appears to visitors on the seized domains.
Source: DoJ
In addition to the law enforcement seizures, the Shadowserver Foundation assisted by working with Internet service providers and Computer Security Incident Response Teams (CSIRTs) to identify infected systems, aid in notifying victims and assisting in remediation.
These actions ended up conducted in coordination with Operation Endgame, a multinational law enforcement initiative targeting the dismantling of malware cybercriminal services.
Click here for more information regarding Operation Endgame.