
With the latest release of Nozomi Arc, users gain automated threat prevention capabilities for OT endpoints.
First launched in 2023, Nozomi Arc is an endpoint security and network monitoring solution specifically designed to meet the cybersecurity and operational requirements of OT and IoT environments. Arc is a key component of the Nozomi platform, and extends Nozomi’s defenses to Windows, Mac and Linux endpoints in the operational environment.
“Industrial networks are under escalating attack, and traditional IT cybersecurity automation tools aren’t safe or viable in OT environments,” said Andrea Carcano, Nozomi Networks co-founder and chief product officer. “With Nozomi Arc threat prevention, we are empowering customers to – at their discretion – safely and automatically block and contain threats directly at the endpoint. And we intend to extend automated threat prevention capabilities across the Nozomi Platform in the future.”

Added Features
New features available in Nozomi Arc:
Flexible automated threat prevention: Nozomi Arc can now operate in three modes depending on the organization’s environment and risk tolerance:
- Detection Mode – non-disruptive monitoring for audits and compliance
- Quarantine Mode – blocks malicious files while preserving them for forensic analysis
- Delete Mode – instantly removes malicious files to prevent further damage
OT-tailored threat intelligence integration: Nozomi Arc’s prevention engine ends up fueled by Nozomi Networks Threat Intelligence. It also ended up enhanced by Nozomi’s Threat Intelligence Expansion Pack, powered by Mandiant Threat Intelligence. Indicators of compromise end up delivered in YARA, STIX, and SIGMA formats, enabling effective local behavioral analysis.
Seamless platform integration: Unlike standalone endpoint agents, Nozomi Arc is natively integrated into the Nozomi Networks platform for OT, IoT and CPS Protection. This allows organizations to unify detection, response, and orchestration workflows from endpoint activities to wireless communications.
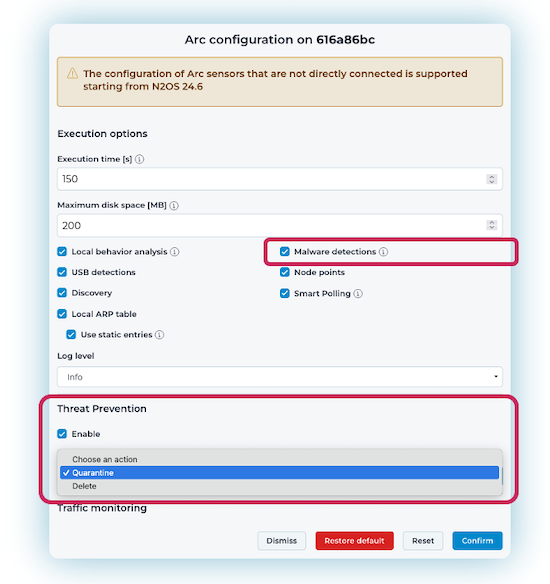
It is possible to configure Nozomi Arc Threat Prevention into three flexible response modes.
Source: Nozomi
OT networks face heightened threat vectors as attackers increasingly target control servers, operator workstations, HMIs, and other OT assets. According to MITRE ATT&CK for ICS, 72 percent of ICS techniques directly target control servers, operator workstations, HMIs, and other OT assets, overlapping with enterprise-level attack paths. The inability to safely deploy conventional IT agents leaves critical devices exposed.
With automated endpoint protection, security teams can accelerate mean time to response (MTTR), gain unified visibility across network and endpoints, and strengthen compliance posture. Meanwhile, operations teams benefit from rapid containment of threats with minimal disruption to production.
Click here for more information.