
It is possible to decrypt the contents of telephone calls if an attacker is in the same radio cell as their target, whose mobile phone they called immediately following the call they wanted to intercept, said researchers from the Horst Görtz Institute for IT Security (HGI) at Ruhr-Universität Bochum. They exploit a flaw that some manufacturers made in implementing the base stations.
The vulnerability affects Voice over LTE, the telephone standard used for almost all mobile phone calls if they are not made via special messenger services. When two people call each other, a key is generated to encrypt the conversation.
“The problem was that the same key was also reused for other calls,” said David Rupprecht. So, if an attacker called one of the two people shortly after their conversation and recorded the encrypted traffic from the same cell, he or she would get the same key that secured the previous conversation.

“The attacker has to engage the victim in a conversation,” Rupprecht said. “The longer the attacker talked to the victim, the more content of the previous conversation he or she was able to decrypt.” For example, if attacker and victim spoke for five minutes, the attacker could later decode five minutes of the previous conversation.
In order to determine how widespread the security gap was, the IT experts tested a number of randomly selected radio cells across Germany.
It turns out, the security gap affected 80 percent of the analyzed radio cells. By now, the manufacturers and mobile phone providers have updated the software of the base stations to fix the problem.
“We then tested several random radio cells all over Germany and haven’t detected any problems since then,” Rupprecht said. Still, it can’t be ruled out that there are radio cells somewhere in the world where the vulnerability occurs.
In order to track them down, the Bochum-based group has developed an app for Android devices. Tech-savvy volunteers can use it to help search worldwide for radio cells that still contain the security gap and report them to the HGI team.
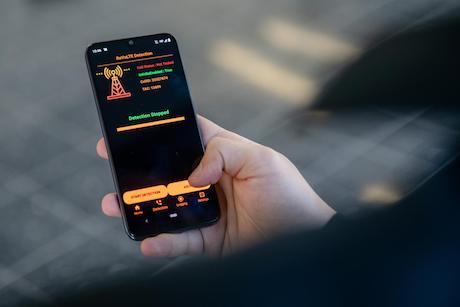
Using this App, tech-savvy volunteers can help search for radio cells that still contain the security vulnerability.
Source: RUB, Marquard
The researchers forward the information to the worldwide association of all mobile network operators, GSMA, which ensures the base stations are updated. Click here for additional information. http://www.revolte-attack.net
“Voice over LTE has been in use for six years,” Rupprecht said. “We’re unable to verify whether attackers have exploited the security gap in the past.” He is campaigning for the new mobile phone standard to be modified so that the same problem can’t occur again when 5G base stations are set up.