
By Gregory Hale
Should a manufacturer patch or not patch if they have a vulnerability in their system? That question has been floating around the industry for years, if not decades. And the answer is: Who knows?
“The ever-growing volume of reported vulnerabilities highlights continued efforts to secure the ICS systems critical to our nation’s energy, manufacturing, water, and transportation infrastructure,” said Jori VanAntwerp, SynSaber chief executive and co-founder in a report entitled, Industrial CVE Retrospective, 3 Years of CISA Advisories 2020 – 2022, by industrial cybersecurity provider, SynSaber.
“The growing focus and regulation come with additional administration and reporting requirements for an already overstretched ICS workforce. Owners and operators in critical infrastructure are being asked to analyze, mitigate, and report on new and existing vulnerabilities,” VanAntwerp said. “But is the uptick in vulnerability reporting directly tied to escalating industrial threats?”

Applicable: Does this apply to my environment?
Without an up-to-date asset inventory, this may not be a factor easily discovered. Each CISA Advisory will have a section titled “affected products” that will list in some detail the exact product, software, and versions affected by the reported vulnerability.
Critical: Is this critical in the context of my environment and systems?
Although CVSS scoring shouldn’t be the only indicator for prioritization, it can be useful in stack ranking CVEs that meet applicability criteria.
Fixable: Is there a permanent fix I can deploy in my environment?
This category can be very complex, as industrial systems may not have straightforward patch management capabilities like in enterprise environments. Fixable, in this case, is a combination of criteria that include:
- Software patch, firmware, or upgrade available from the OEM
- Configuration that is attainable and not disruptive to operations
- Doesn’t require a whole system, subsystem, or architecture change
Also, it is very easy to get caught in the hype of a vulnerability being found in your system. While at one point the fear of having a vulnerability could supersede any kind of normal rational thought, but in reality, a significant number of reported CVEs have exploit paths that are not practical in ICS, according to the report.
CVEs that require user interaction or local/physical access to the system are exceedingly difficult to practically exploit. Due to the nature of industrial control system operations and architecture, network accessibility and potential user interaction have a lower probability of occurrence versus enterprise IT, according to the report.
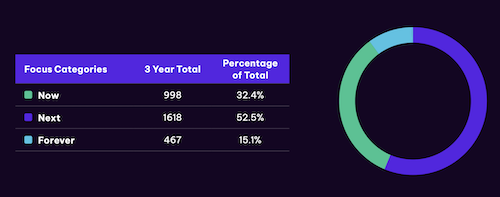
There are three types of CVEs: Now, which should be addressed immediately; Next, which are more complex from a remediation perspective but still require attention, and Forever which have architectural and interoperability impacts and one cannot simply patch away.
Source: SynSaber
Common exploitation vectors like direct Internet access, email, and web browsers are not typically present in industrial control environments.
Critical CVEs Rise
With an increase in vulnerabilities reported, it is interesting to note the severity of critical CVEs increased in 2022 to 296 from 186 the previous year, while high-rated CVEs decreased to 632 from 678.
Siemens led the pack in CVEs reported last year with 544. Hitachi was a distant second with 64, Mitsubishi Electric had 31 and Rockwell Automation had 18. There were 657 overall OEM CVEs reported last year.
As a side note: Just because Siemens had so many listed CVEs, it does not mean their product is not secure. To the contrary, they have a dedicated staff to finding vulnerabilities, and they will report on them and then fix them. It ends up being a volume thing, where Siemens has so much product out there and they have been very diligent in cleaning it up.
The volume of CVEs reported via CISA ICS Advisories and other entities is not likely to decrease. It’s important for asset owners and those defending critical infrastructure to understand when remediations are available, and how those remediations should be implemented and prioritized.
Merely looking at the sheer volume of reported CVEs may cause asset owners to feel overwhelmed, but the figures seem less daunting when we understand what percentage of CVEs are pertinent and actionable versus which will remain “forever-day vulnerabilities,” at least for the time being, according to the report.
What Does It Mean?
Does an increase in reported CVE numbers indicate any of the following?
- Industrial control system security is trending downwards
- Industrial threats are trending upwards
Not necessarily. What it could indicate is product security teams are increasing their internal reporting and public disclosure of vulnerabilities to the community.
More transparency is typically a great thing when it comes to vulnerability research, but the community at large must be cautious and skeptical of companies or individuals running up the numbers for the sake of fame and fortune.
Understanding the overall metrics, analysis methodologies, and considerations of ICS CVEs is a great step toward empowering the industrial community.
Click here for more on the report.