
Diverse approaches from all the agencies originally did not collectively address the dynamic nature of the current cyber threat environment, the complexity of the digital ecosystem, and the pace of technology modernization.
As a result, despite concerted efforts to adapt and protect against cyberattacks, the FCEB remains vulnerable.
CISA’s FCEB Operational Cybersecurity Alignment (FOCAL) Plan outlines how agencies can work toward this by adopting proven practices along the spectrum – from prevention to incident detection and response –and identifying collective goals for security across the federal enterprise.

Moreover, in recent years, the federal government’s executive orders, policies, and directives have driven significant cybersecurity improvements at federal agencies in response to this dynamic threat environment.
Additionally, as the Office of Management and Budget (OMB) and Office of the National Cyber Director (ONCD) continue to shape national cybersecurity policy and set strategic expectations for federal cybersecurity, CISA is the operational lead, ensuring the enterprise has the necessary capabilities to meet those expectations.
The FOCAL Plan is a strategic document that includes broad organizing concepts for federal cybersecurity and a tactical one that provides specific actionable steps agencies can take in the next year to improve their cybersecurity posture.
This plan identifies areas in need of standardization and consistency (priority areas), enabling the federal enterprise’s cyber defense apparatus during steady state operations and facilitating rapid response when urgent situations require interagency action.
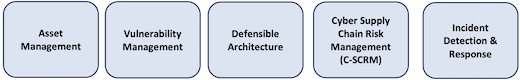
Five FOCAL priority areas.
Source: CISA
The FOCAL Plan is not a comprehensive or exhaustive list of everything that an agency or CISA must accomplish. Rather, it focuses resources on those actions that substantively advance operational cybersecurity improvements and alignment goals.
This plan falls into five priority areas that CISA considers essential for positioning efforts across the federal cybersecurity landscape and that align with agencies’ Federal Information Security Modernization Act metrics and reporting requirements.
The five areas include:
Asset Management: Full understanding of the cyber environment, including both operational terrain and interconnected assets, is foundational for the federal enterprise.
Vulnerability Management: What constitutes an agency’s enterprise has evolved over the years, particularly as the attack surface has expanded and grown more complicated. One key to vulnerability management is to acquire and maintain the initiative within one’s environment.
Defensible Architecture: As federal agencies modernize their technology, the importance of keeping every new component working seamlessly with the existing systems can create new cybersecurity challenges. This is why agencies must intentionally build a defensible architecture.
Cyber Supply Chain Risk Management: The U.S. government has taken meaningful steps to improve how it manages significant risk to the cyber supply chain.
Incident Detection and Response: The maturity of incident detection and response capabilities varies between organizations, yet even the most effective Security Operations Centers (SOCs) are unable to detect all intrusions. Incident detection and response is a critical component of an effective cybersecurity program, as no protective measures are likely to fully prevent adversaries’ access to federal IT assets.
Click here for more on the new cyber defense plan.