
Manufacturing was most heavily impacted by ransomware, followed by the technology and retail/wholesale industries, according to the GuidePoint Research and Intelligence Team’s (GRIT) annual Ransomware & Cyber Threat Report. Surprisingly, and despite being a cybersecurity nightmare for years, the healthcare sector dropped out of the top three most affected industries by the end of the year.
Manufacturing remained the industry most frequently impacted by ransomware groups in 2024, with 67 percent of the distinct ransomware groups tracked by GRIT claiming at least one victim within the industry over the course of the year.
Understanding the incredible year-over-year growth going back a half-decade, researchers expected another year of ransomware growth, But, in reality the persistence and effectiveness of international law enforcement operations, showed minimal year-over-year growth of victim volume of 8.72 percent, which is quite a drop 2022-2023’s 76.8 percent growth.

Other Highlights
Other findings from this year’s report include:
- A record high of ransomware victims, with over 1,600 ransomware victims in Q4 2024 alone, the largest number recorded in a single quarter since the report’s inception.
- A 40 percent year-over-year increase in active threat groups, illustrating a continually-developing threat landscape. GRIT identified over 88total active threat groups in 2024, including 40 newly observed adversaries.
- An average of 93 ransomware victims ended up posted per week on the dark web. RansomHub claimed the largest number of victims in 2024, displacing LockBit as the most active ransomware group for the first time since 2021.
- The United States remains a top geographic target for ransomware attacks. In 2024, more than half (52 percent) of ransomware victims were in the U.S.
- An average of 110 Common Vulnerabilities and Exposures (CVEs) published per day, underscoring the overwhelming volume and velocity of information which cybersecurity teams are facing. Almost 40,000 CVEs ended up reported in 2024, a 43 percent increase from 2023.
- Nearly 44 percent of vulnerabilities were rated “High” or “Critical” severity. However, threat actors continue to rely on historical vulnerabilities from preceding years.
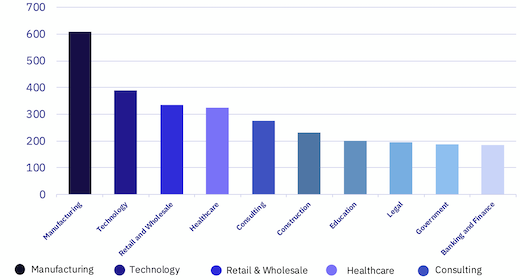
Industries that felt the most impact by ransomware in 2024.
Source: GuidePoint Security
“Throughout the year, we also witnessed multiple instances of significant international law enforcement operations that dealt heavy blows to various threat actors and their infrastructures,” said Jason Baker, lead threat analyst at GuidePoint. “While the fight is far from over, the enduring effects of these law enforcement campaigns suggest that we’re developing more effective and sustainable strategies to combat our adversaries – and we anticipate continued progress in 2025.”
Diverse Acess Vectors
Initial access vectors observed in 2024 for ransomware and data extortion remain diverse, with stolen valid credentials and exploitation of new and historical vulnerabilities remaining among the most common.
The risk posed by these access vectors is disproportionately experienced by small- to-midsized businesses (SMBs) that may lack the financial resources to detect and respond to them in a timely manner, according to the report. Large enterprises, however, remain susceptible to the sophisticated and persistent approach favored by some established attack groups.
For more information, click here to register for the report.