
While video conferencing platforms like Zoom and Microsoft Teams have become essential for work, education, and even social connections, security remains questionable.
While these platforms offer controls such as disabling cameras and muting microphones to safeguard user privacy, computer scientists at SMU discovered attackers can actively and covertly probe a user’s physical location by exploiting the two-way audio channels of video conferencing apps.
In a study published by the IEEE, the research team tested popular apps such as Zoom and found proposed attacks were able to recognize user’s locations or location contexts with 88 percent accuracy, whether the user was in the same place multiple times or had never been there before.

Privacy Concern
“The results raise a severe privacy concern since any video conferencing participant could invade each other’s location privacy easily without malware installation,” said SMU principal investigator Chen Wang, O’Donnell Foundation Endowed Professor of computer science at SMU Lyle School of Engineering.
This type of cybersecurity – known as “sniffing location privacy” – is particularly alarming because there’s very little users can do to secure videoconferencing, Wang said.
“Even a vigilant user who carefully unmutes the microphone only when speaking remains vulnerable: An adversary can exploit the few silent seconds between unmuting and muting, since people naturally leave margins to ensure their speech is fully heard,” he noted. “Furthermore, we find that when a user speaks, echo sounds return with higher energy, because video conferencing systems apply acoustic suppression to silent user ends to eliminate meaningless feedback.”
As a result, the user’s speech effectively amplifies the malicious signal feedback.
Another issue is the probing sounds can be as short as 100 milliseconds, giving attackers sufficient information before a victim would have time to notice.
Defense Algorithms
Wang and his team are currently working on defense algorithms that can end up deployed at the video conferencing server to detect and delete suspicious probing sounds before forwarding audio to participants, along with other ways to defend against an adversary being able to sense our surroundings and see where we are.
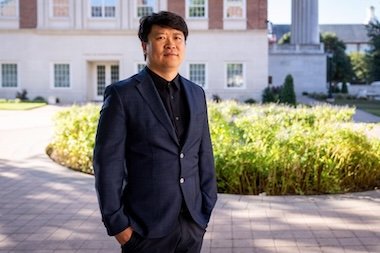
SMU computer science professor Chen Wang found that even with cameras turned off and virtual backgrounds in use, video meeting participants can still be vulnerable to privacy intrusions.
Source: Southern Methodist University, Jeffrey McWhorter
SMU researchers identified two types of echo attacks that are non-invasive enough to go unnoticed by the victim: The in-channel echo attack, which uses carefully crafted signals to bypass echo cancellation, and the off-channel echo attack, which hijacks everyday sounds like email notifications to slip past defenses undetected.
These methods could allow a thief or spy, for instance, to learn when you are at home. An adversary can also determine where the user is whenever they meet online, even if the user is using a virtual background.
The research team’s findings come from six-month experiments at 12 different locations, ranging from homes and offices to vehicles and hotels.
“We all know that video conferencing systems utilize echo cancellation functions to suppress audio feedback and ensure call quality,” Wang said. “However, we find that an adversary can leverage generative AI encoders to counteract such echo cancellation mechanisms and extract stable location embeddings from severely suppressed echo signals, even though they are nearly imperceptible to human listeners.”
Click here to view the paper.